Free On-Site Cybersecurity & IT Audit for Metro Detroit Businesses
A free on-site cybersecurity audit in Detroit can help uncover overlooked security risks, aging technology, and IT problems before they disrupt your business. Cyber Protect LLC offers qualifying Southeast Michigan businesses a complimentary 35-point Cybersecurity & IT Inspection that combines an in-person technology review with agreed internal and external security checks. We look for vulnerabilities, outdated equipment, configuration issues, weak account protections, and gaps that could contribute to downtime or data exposure. You’ll receive clear findings, practical recommendations, and a straightforward explanation of what matters most. No cost. No obligation. No scare tactics. Just answers and clarity.A Real On-Site Inspection, Not Just an Online Questionnaire
A free on-site cybersecurity audit in Detroit goes beyond what an online questionnaire can tell you. An online quiz cannot verify that a backup restores, a workstation is updated, or your network settings are appropriate. Cyber Protect LLC combines an on-site conversation with hands-on observations and approved technical checks. We review what is working, what could be improved, and what needs attention first.
What Does Our Free 35-Point Inspection Cover?
Cybersecurity
Endpoint protection, firewall and network controls, account security, multifactor authentication, email defenses, phishing awareness and relevant risk management practices.
IT Services
Computers and servers, patching, equipment lifecycle, inventory, vendor support, internet connectivity, wireless coverage, power protection and technology costs.
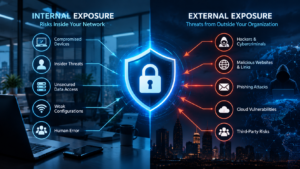
Internal and External Exposure
Authorized network scanning and review of agreed internet-facing systems, with findings interpreted in context.
Continuity and Readiness
Backups, recovery practices, cyber insurance considerations and safeguards relevant to applicable requirements.
Each of the 35 inspection points may involve a question, hands-on observation, technical evaluation or approved testing activity. The exact checks depend on the business and the agreed scope.
What Our 35-Point Inspection Process Looks For
The exact tests depend on your environment, available access and the agreed scope. Typical inspection areas include:
-
External attack surface: publicly reachable services, exposed ports, domain and email authentication configurations, and scanner-identified issues requiring validation.
-
Internal network: authorized vulnerability scanning, network equipment, firewall configuration, Wi-Fi separation, aging devices and avoidable exposure.
-
Computers and servers: supported operating systems, patch status, endpoint protections, encryption, local privileges and inventory completeness.
-
Email and cloud: Microsoft 365 or Google Workspace protections, multi-factor authentication, risky settings, account access and shared-data exposure.
-
Backups and business continuity: coverage, retention, independence of backups, restoration evidence, outages and recovery readiness.
-
IT operations: monitoring, documentation, vendor responsibilities, asset lifecycle, onboarding/offboarding, remote access and security awareness.
-
Compliance readiness: review of relevant safeguards and supporting evidence for frameworks and obligations applicable to your business.
What Will Your Business Receive?
-
01
A scheduled on-site discussion about your technology, priorities, and known concerns.
-
02
Agreed internal and external security checks, including authorized scan findings where appropriate, with scope and limitations documented.
-
03
A plain-English, executive-level summary of observed risks, strengths, and issues needing further validation.
-
04
Prioritized recommendations covering immediate and longer-term improvements, which you can discuss with your own IT provider or Cyber Protect.
-
05
Guidance on how findings relate to security best practices and compliance-readiness needs.
-
06
An opportunity to ask questions and discuss next steps, with no obligation to purchase services.
Why Request an Independent IT Security Inspection?
Your current IT provider may be doing good work. A second assessment can still uncover outdated devices, incomplete backups, configuration mistakes, unnecessary spending or account privileges that have grown too broad. Our goal is to give you evidence and a realistic plan, not manufacture problems.
How the Free On-Site Inspection Works
Request an inspection using the short form or call us.
We confirm your location, eligibility, business environment and the work to be performed.
You approve the assets, access and timing for any technical testing.
We conduct the agreed on-site inspection and explain the findings.
You decide whether to address the recommendations internally, with your provider or with Cyber Protect.
Built Around Recognized Security Best Practices
Our inspection can help identify technical and operational gaps relevant to widely recognized references such as the NIST Cybersecurity Framework, CIS Critical Security Controls and, where applicable, HIPAA Security Rule safeguards, FTC Safeguards Rule requirements or cyber insurance questionnaires. We tailor the review to the systems and requirements you actually have. A free inspection is not a penetration test, formal risk assessment, legal opinion, audit attestation or certification of compliance.
Local Cybersecurity & IT Inspections for Michigan Businesses
Cyber Protect serves qualifying organizations in Warren, Macomb County and the greater Metro Detroit area, including legal practices, healthcare offices, accounting firms and other small and midsize businesses. If you are renewing cyber insurance, changing IT providers, expanding your workforce or simply unsure of your current protection, an inspection can help establish your next priorities.
Frequently Asked Questions
Is the 35-point cybersecurity and IT inspection really free?
Yes, for qualifying businesses within our approved service area and agreed limited inspection scope. There is no requirement to purchase services.
Does the inspection include internal and external vulnerability scanning?
It can include approved internal network checks and an assessment of agreed internet-facing systems. We confirm authorization, assets and testing windows before scanning.
Will the inspection disrupt daily operations?
We plan checks to limit disruption, but technical testing cannot be guaranteed risk-free. We agree on boundaries and timing first.
Can the inspection tell us if we meet HIPAA or NIST requirements?
We can flag gaps relevant to applicable practices and safeguards. This introductory inspection is not a formal compliance determination, penetration test, certification or legal opinion.
Do we have to replace our IT provider?
No. Our findings can help you work with your existing provider or evaluate other options.
Will we receive findings and recommendations?
Will we receive findings and recommendations? body: Yes. We provide an executive-level findings review and prioritized next steps for the agreed free scope. Deeper testing and extensive formal reports may require a separately scoped engagement.
Know Where Your Business Stands
Schedule Cyber Protect’s free 35-point on-site Cybersecurity & IT Inspection. Find out what is protected, what needs attention and how to reduce avoidable downtime and security risk.